
Pass-through, never stored
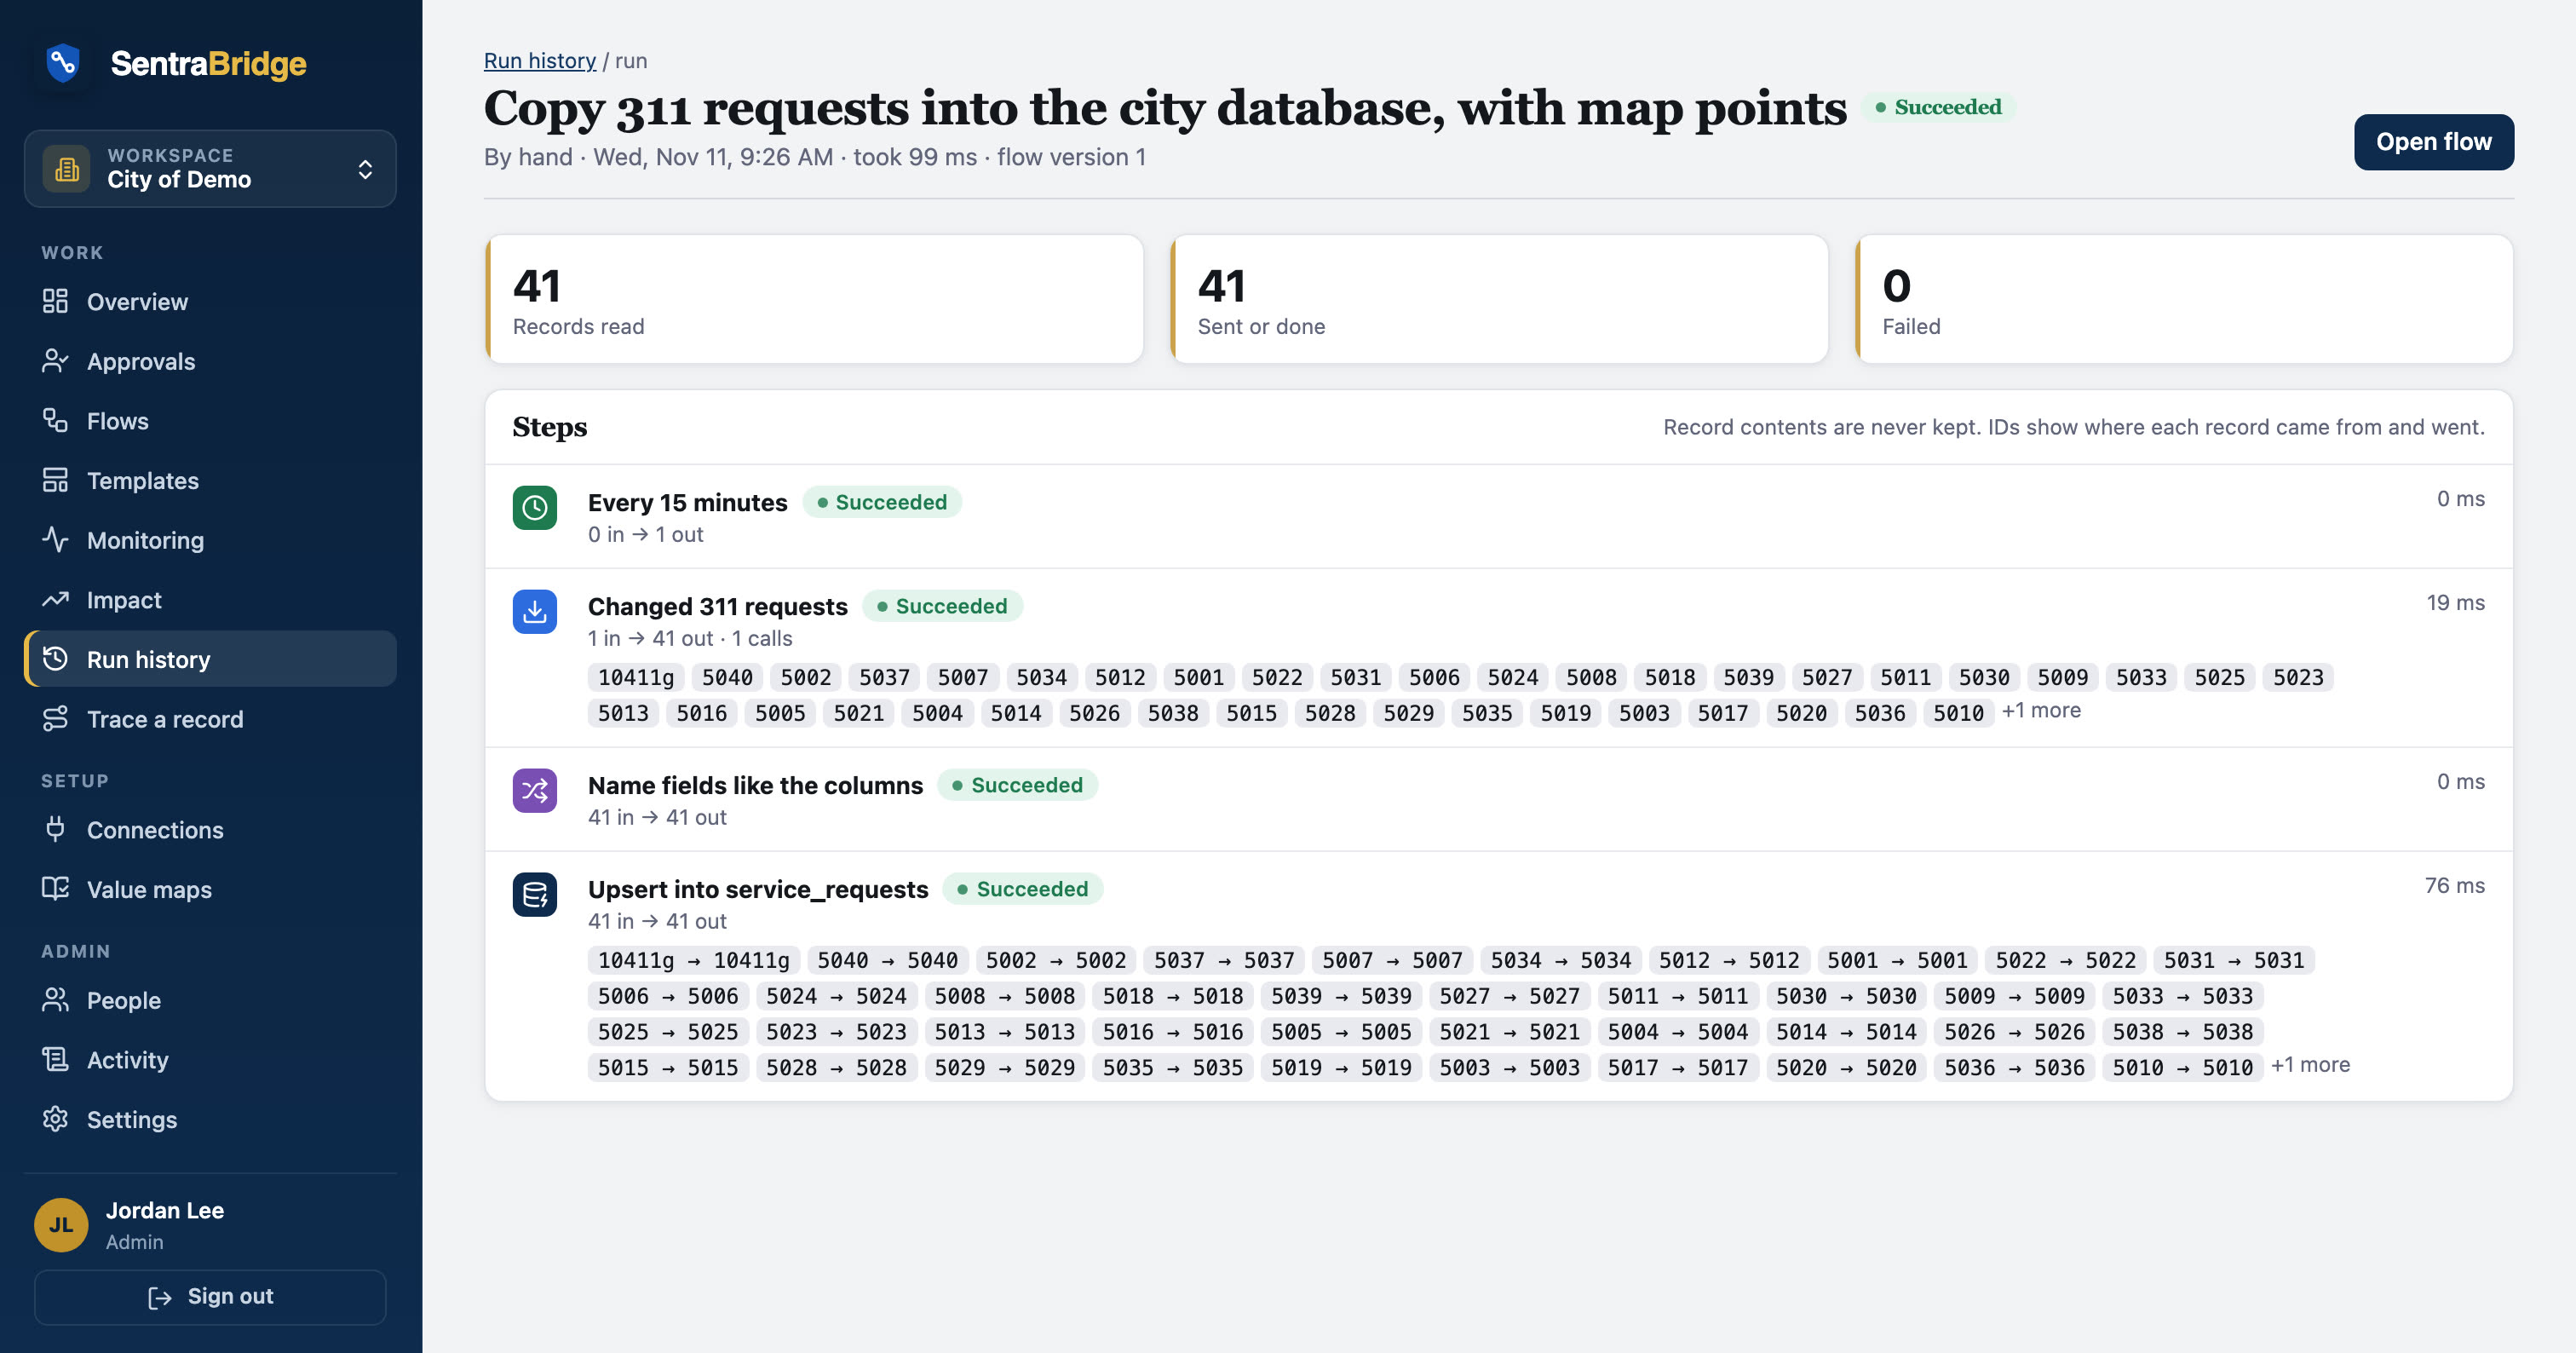
Records are read into memory, changed and delivered, then dropped when the run ends. Never written to a database, queue or log.
The safest copy of residents' data is the one that doesn't exist. SentraBridge moves records between your systems without keeping them, and logs what happened without logging what was in them.
Records are read into memory, changed and delivered, then dropped when the run ends. Never written to a database, queue or log.
Run history keeps counts, timings, record IDs and error text with emails and phone numbers masked. You choose how long it's kept, from 7 days to 10 years.
HTTPS to every API, TLS to databases (on by default for SQL Server), and SSH for files with each server's host key pinned.
Passwords, tokens and keys are encrypted and never returned to the browser after saving.
Authenticator-app codes with recovery codes, required for everyone if you choose. Weak and commonly used passwords are refused.
Sign in through your own identity provider (SAML: Microsoft Entra ID, Okta, ADFS). SCIM adds and removes people automatically; removed people lose access at once.
Limit sign-in, API tokens and AI assistants to your networks. Webhooks can have their own list. Calls to private addresses are refused unless an admin allows that server.
Every agency has its own workspace, and people can be limited to their department's flows, connections and runs.
Every change is logged with a fingerprint of the entry before it, so edits or deletions are detected. Export it, or stream it to your SIEM by syslog, OpenTelemetry or webhook.
Set how long history and logs are kept. A legal hold stops removal for the whole workspace or one flow. One click exports everything kept, for a records request.
Mask, tokenize or encrypt fields like SSNs and account numbers inside a flow. Encryption is AES-256, optionally with a key held in your own AWS KMS.
The SentraBridge Relay runs on your network and only calls out, so internal databases and file servers are reachable with no inbound ports.
Custom queries must be a single SELECT in a read-only transaction. A flow paused for approval keeps record IDs, not contents.
Signatures are checked for every Sentra product, plus generic HMAC and token checks. Webhook messages are never queued.
The AI builder sees settings and field names. The Ask AI step sends only listed fields, after an admin allows it. Every AI and MCP call is logged: who, when, which model or tool.
SentraBridge doesn't claim certifications it doesn't hold. These features map to what CJIS, IRS 1075 and state cloud programs ask of the systems you run; your auditors decide what's in scope.
Multi-factor sign-in for every account, 256-bit encryption, audit logs you can export and forward, network allow-lists, and self-hosting or the relay so criminal justice data stays on your network.
No stored copies of records to produce. Retention you set, legal holds, AI and MCP call logs kept as records, and a one-click export of everything SentraBridge keeps.
Reconcile with control totals between billing, the ledger and the bank, and positive pay files, with a log that shows it wasn't changed.
The app is checked against WCAG 2.1 AA with automated tests, and flows can be wired from the keyboard. Ask for our VPAT self-assessment.
To call your systems SentraBridge must keep connection settings, field maps and encrypted credentials. Run history holds metadata only: when, which flow, record IDs on each side, HTTP status, duration and masked error text.
Each activity entry carries a fingerprint of the one before it. Anyone with admin rights can check the whole chain in one click, export it as CSV or JSON, or send each entry to your security tools as it happens.
| entry | time | what happened | fingerprint ← previous |
|---|---|---|---|
| #1042 | 09:14 | Pat L. changed the flow “Payments to ledger” | 3f9a… ← c81e… |
| #1043 | 09:20 | Admin turned on two-step sign-in | 77d0… ← 3f9a… |
| #1044 | 09:31 | Records export made (Oct 1–31) | b2c4… ← 77d0… |
The SentraBridge Relay runs inside your network and only connects out. It reaches the hosts you list and nothing else, and its jobs are encrypted and deleted on completion. Or run all of SentraBridge on your own servers.
CSP hosts SentraBridge on US-based cloud infrastructure, or your IT team runs it on your own servers, including networks with no internet access. The web app uses no outside content networks.
The product's automated tests check that preview never writes, that run history contains no record values or tokens, that file contents never reach the database, and that webhook messages are never queued.
| when | flow | path | result |
|---|---|---|---|
Mon 7:15 | 311 triage | Read → Clean and check → New request? → Create Scheduler visit | sent |
Mon 7:15 | 311 triage | Update the database copy | upserted |
Tue 2:00 | Nightly CSV to SFTP | Write CSV · requests-2026-11-10.csv | written |
Wed 7:00 | Operations digest | Combine → Count by source → Email | counted |
We don't claim certifications we don't hold. Ask us for our current security documentation, and we'll answer your questionnaire directly. Self-hosting keeps everything inside your own controls.
There are no stored records to produce. Run history holds metadata (IDs, counts, times), which you can review yourself.
On US-based cloud infrastructure run by CSP, or on your own servers. We don't name our hosting provider on public pages; ask us directly during procurement.
Platform staff manage clients for support from a separate staff-only console. Your workspace's connections and secrets are encrypted, and secrets are never shown again after saving. Staff actions are recorded in the activity log.
Yes. Connect SAML single sign-on (Microsoft Entra ID, Okta, ADFS and others) and SCIM directory sync, and require two-step sign-in for anyone who uses a password.
Yes. Run the SentraBridge Relay on your network: it calls out to SentraBridge, so you open no inbound ports, and it reaches only the hosts you list. Or self-host SentraBridge entirely.
Yes: a VPAT 2.5 self-assessment against WCAG 2.1 AA. Ask us for the current version.
We'll walk your IT and security team through how SentraBridge handles data, and answer your questionnaire.